
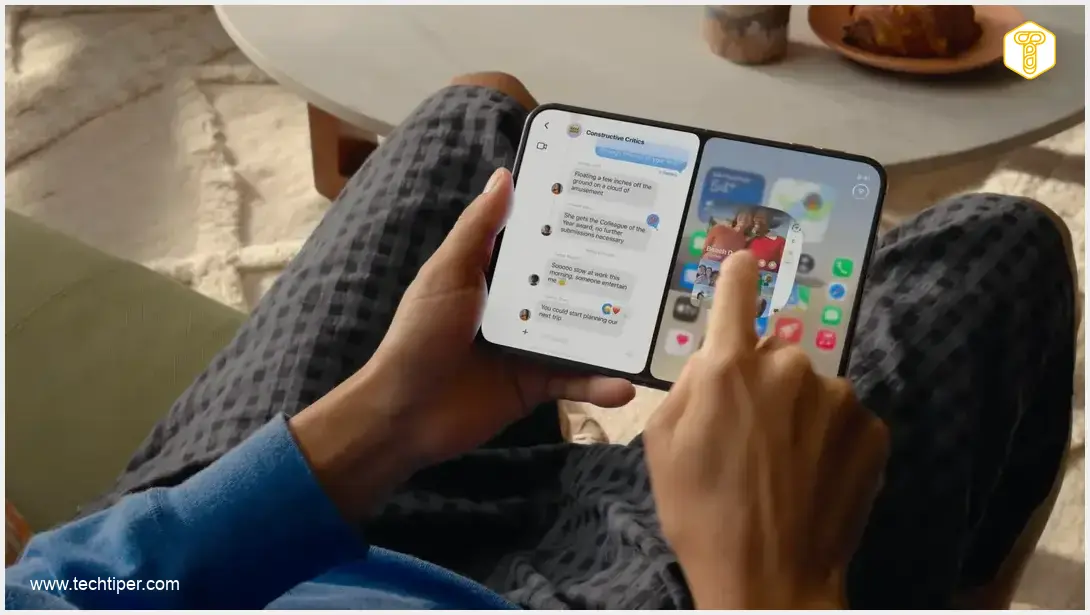
The highly anticipated launch of the iPhone Duo has unfortunately created a new opportunity for cybercriminals. Scammers are now deploying a dangerous form of phishing designed to steal personal data, passwords, and even access to cryptocurrency wallets. This sophisticated attack, known as DarkSword, is particularly insidious as it can compromise older iPhone models simply by visiting a malicious website, without requiring any app installations or download confirmations.
This article will delve into the mechanics of this scam, explain the DarkSword exploit, outline the data at risk, and provide crucial advice on how to protect yourself from becoming a victim.
Contents
Understanding the iPhone Duo Pre-Order Scam
Cybercriminals have meticulously crafted fake websites that mimic the official Apple Store. These fraudulent sites promise eager consumers the chance to pre-order the iPhone Duo ahead of its official release, often luring them with additional incentives like a $500 voucher. To create a sense of urgency and authenticity, these pages typically feature a countdown timer indicating the supposed end of the promotion and a form designed to collect personal information.
However, it’s crucial to understand that the official pre-orders for the iPhone Duo are not scheduled to begin until October 16, 2026, with retail sales following on October 23, 2026. Therefore, any offer to “pre-order” Apple’s first foldable smartphone before these dates is unequivocally a scam. Such tactics are common in online fraud, often seen in fake ads and TikTok scams designed to exploit user excitement.
How the DarkSword Exploit is Triggered
The danger lies in the underlying exploit. When a user with a vulnerable iPhone visits one of these specially prepared fraudulent websites, a chain of DarkSword exploits, specifically tailored for the Safari browser, is automatically activated. If the script doesn’t immediately recognize the browser, users might see a message about an unsupported browser with a button prompting them to reopen the link in Safari, further guiding them into the trap.
What makes this attack particularly dangerous is its stealth. The exploit operates silently in the background, requiring no interaction from the user – no clicks, no confirmations, nothing. An invisible frame on the webpage discreetly checks the device’s iOS version and then loads the appropriate attacking components. These components attempt to bypass the device’s security measures to gain unauthorized access to data.
DarkSword: The Dangerous iOS Exploit
DarkSword refers to a collection of zero-day vulnerabilities in iOS. These vulnerabilities allow for remote control over a device simply by visiting a malicious website. According to reports from leading cybersecurity firms, this specific variant of DarkSword is known to affect iOS systems from version 18.4 to 18.7. It has previously been utilized by commercial spyware vendors, including PARS Defense, a Turkish company, highlighting its sophistication and the serious threat it poses.
In March 2026, estimates suggested that as many as 270 million devices could have been running on these vulnerable iOS versions, making them potential targets for widespread attacks. The threat primarily impacts older iPhone models that have not been updated to the latest security patches released by Apple. Staying informed about such threats is vital for digital safety; for more details on this specific exploit, refer to our comprehensive iPhone DarkSword Exploit Security Warning.
What Data is at Risk?
The payload, which is the final component of the attacking code, is meticulously designed to extract as much sensitive information from the compromised device as possible. Attackers can gain access to a wide array of personal data, including:
- Saved passwords from the iOS keychain
- Message history and call logs
- Contact lists
- Email content
- Photos and other media files
- Information about installed applications
Of particular concern is the fact that this attack also targets the contents of Apple Notes and, critically, cryptocurrency wallet data. Access to these sensitive areas can directly lead to significant financial losses for the victim.
Cybersecurity experts, including those from Malwarebytes, emphasize that victims do not even need to fill out a form on the fake website. Simply opening the malicious site on a vulnerable device is sufficient to initiate the attempt to compromise the phone. If the attack succeeds, criminals can use the acquired data to take over email accounts, Apple IDs, bank accounts, and cryptocurrency exchange accounts. They can also use this information to conduct further phishing campaigns in the victim’s name, perpetuating the cycle of fraud.
How to Protect Yourself
Given the sophisticated nature of these attacks, vigilance and proactive security measures are paramount:
- Verify Sources: Always remember that official iPhone orders are processed exclusively through the Apple Store, authorized retail partners, and reputable cellular network providers and electronics stores. Avoid any random domains that merely resemble official Apple addresses.
- Keep Your Software Updated: Regularly update your iPhone to the latest iOS version. Apple frequently releases security patches to address vulnerabilities like DarkSword. Older, unpatched devices are significantly more susceptible to such exploits.
- Be Skeptical of Deals: If an offer seems too good to be true, it likely is. Be wary of promises for early access, significant discounts, or special vouchers, especially for highly anticipated products like the iPhone Duo.
- Enable Two-Factor Authentication (2FA): Use 2FA on all your critical accounts, including Apple ID, email, banking, and cryptocurrency exchanges. This adds an extra layer of security, making it harder for attackers to gain access even if they steal your password.
- Use Reputable Security Software: While not a complete safeguard against zero-day exploits, using reputable security software on your devices can offer additional protection against known threats and malicious websites.
Frequently Asked Questions (FAQ)
The iPhone Duo scam involves fraudulent websites that impersonate the official Apple Store, offering fake early pre-orders for the unreleased iPhone Duo. These sites are designed to steal personal information, passwords, and financial data by leveraging sophisticated exploits like DarkSword when a vulnerable iPhone visits the page.
DarkSword is a set of zero-day vulnerabilities in iOS that can be triggered simply by visiting a malicious website on a vulnerable iPhone (specifically iOS versions 18.4 to 18.7). It runs in the background without user interaction, bypassing security measures to gain access to sensitive data, including passwords and crypto wallet information.
Immediately update your iPhone to the absolute latest iOS version available. Apple regularly releases security patches to address vulnerabilities. Avoid visiting suspicious websites and be extremely cautious about any unsolicited offers for new devices. If you suspect your device has been compromised, change all your passwords, enable two-factor authentication on all accounts, and monitor your financial statements closely.
Always verify pre-order offers directly through official channels: the official Apple website, authorized Apple retail stores, or your trusted cellular carrier’s official website. Cross-reference information with reputable tech news outlets. Be highly suspicious of any third-party websites or social media ads offering significantly early access, exclusive deals, or asking for unusual payment methods for upcoming Apple products. The official launch dates for new products are always announced directly by Apple.
Source: Cnet, Malwarebytes, Uniladtech. Opening photo: Apple / press materials
About Post Author
